
Real screen · demo data
An auditor checks the bundle offline
The free verifier needs only Node.js: signature and every entry hash verified.
SecOwl 2.1Demo data
How to check it
 Where Trust Begins
Resource
Real screens, a signed evidence bundle and full test results from SecOwl running live, with the files to check them yourself.
The free verifier needs only Node.js: signature and every entry hash verified.
Check it yourself
Download the bundle, the edited copy, the public key and the verifier into one folder. With Node.js installed, run the two commands below. We ran the same commands before publishing and got the results shown.
| File | What it is | Details | Size |
|---|---|---|---|
| evidence-bundle.json | Signed evidence bundle | A 30-day slice of the demo installation's audit ledger (39 entries), signed with its Ed25519 key. | 23 KB |
| evidence-bundle-edited.json | Edited copy of the bundle | The same bundle with one entry changed afterwards (entry 12: the actor), to show that any edit is caught. | 23 KB |
| secowl-public-key.pem | Public key of the demo installation | Proves the bundle came from the installation used for these captures. | 1 KB |
| verify-evidence.js | Offline verifier | SecOwl's verifier for auditors. Needs only Node.js 18 or later; no SecOwl, database or network. | 3 KB |
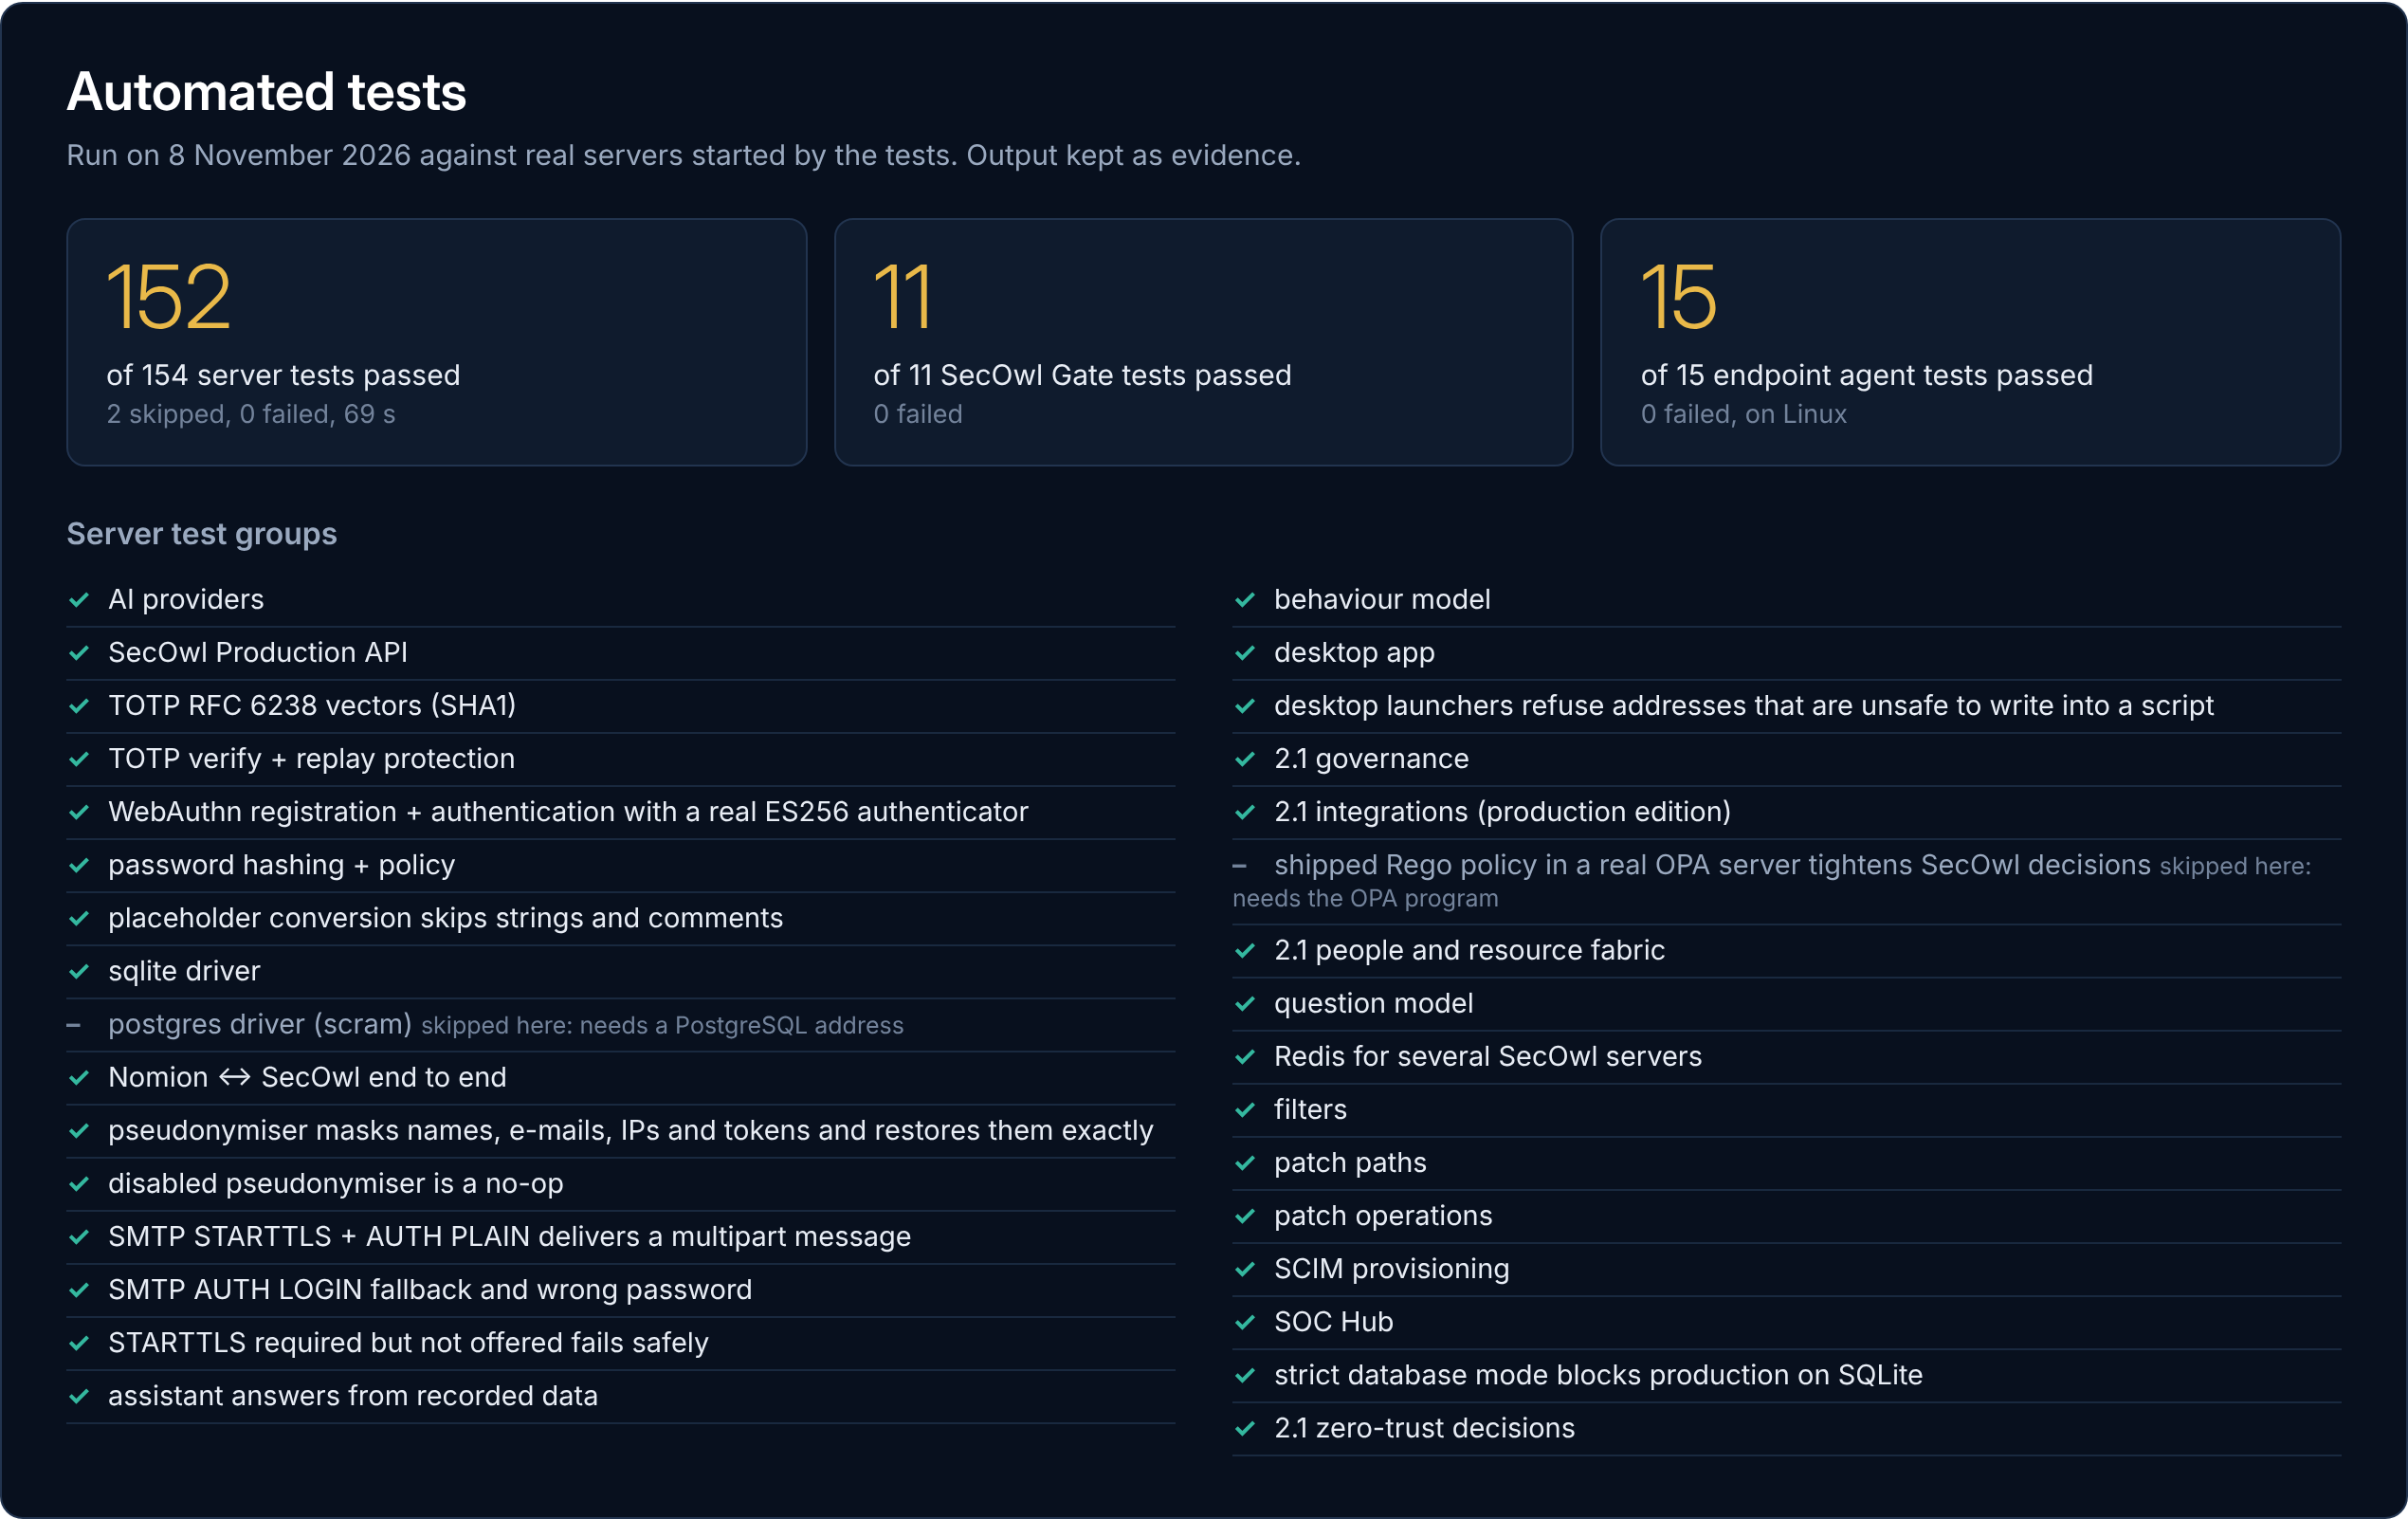
| backend-tests-output.txt | Server test output | Full, unedited output: 152 of 154 passed, 2 skipped. | 31 KB |
| gate-tests-output.txt | SecOwl Gate test output | Full, unedited output: 11 of 11 passed. | 2 KB |
| agent-tests-output.txt | Endpoint agent test output | Full, unedited output: 15 of 15 passed on Linux. | 4 KB |
| report-compliance.pdf | Compliance readiness report (PDF) | Generated by SecOwl for the demo company. | 17 KB |
| report-executive.pdf | Executive security summary (PDF) | Generated by SecOwl for the demo company. | 2 KB |
| report-zero-trust.pdf | Zero-trust decisions report (PDF) | Generated by SecOwl for the demo company. | 8 KB |
1. The original bundle
node verify-evidence.js evidence-bundle.json --key secowl-public-key.pemExpected: VALID: signature and every entry hash verified.
2. The edited copy
node verify-evidence.js evidence-bundle-edited.json --key secowl-public-key.pemExpected: INVALID: the signature does not match, and entry #12 content changed after it was recorded.
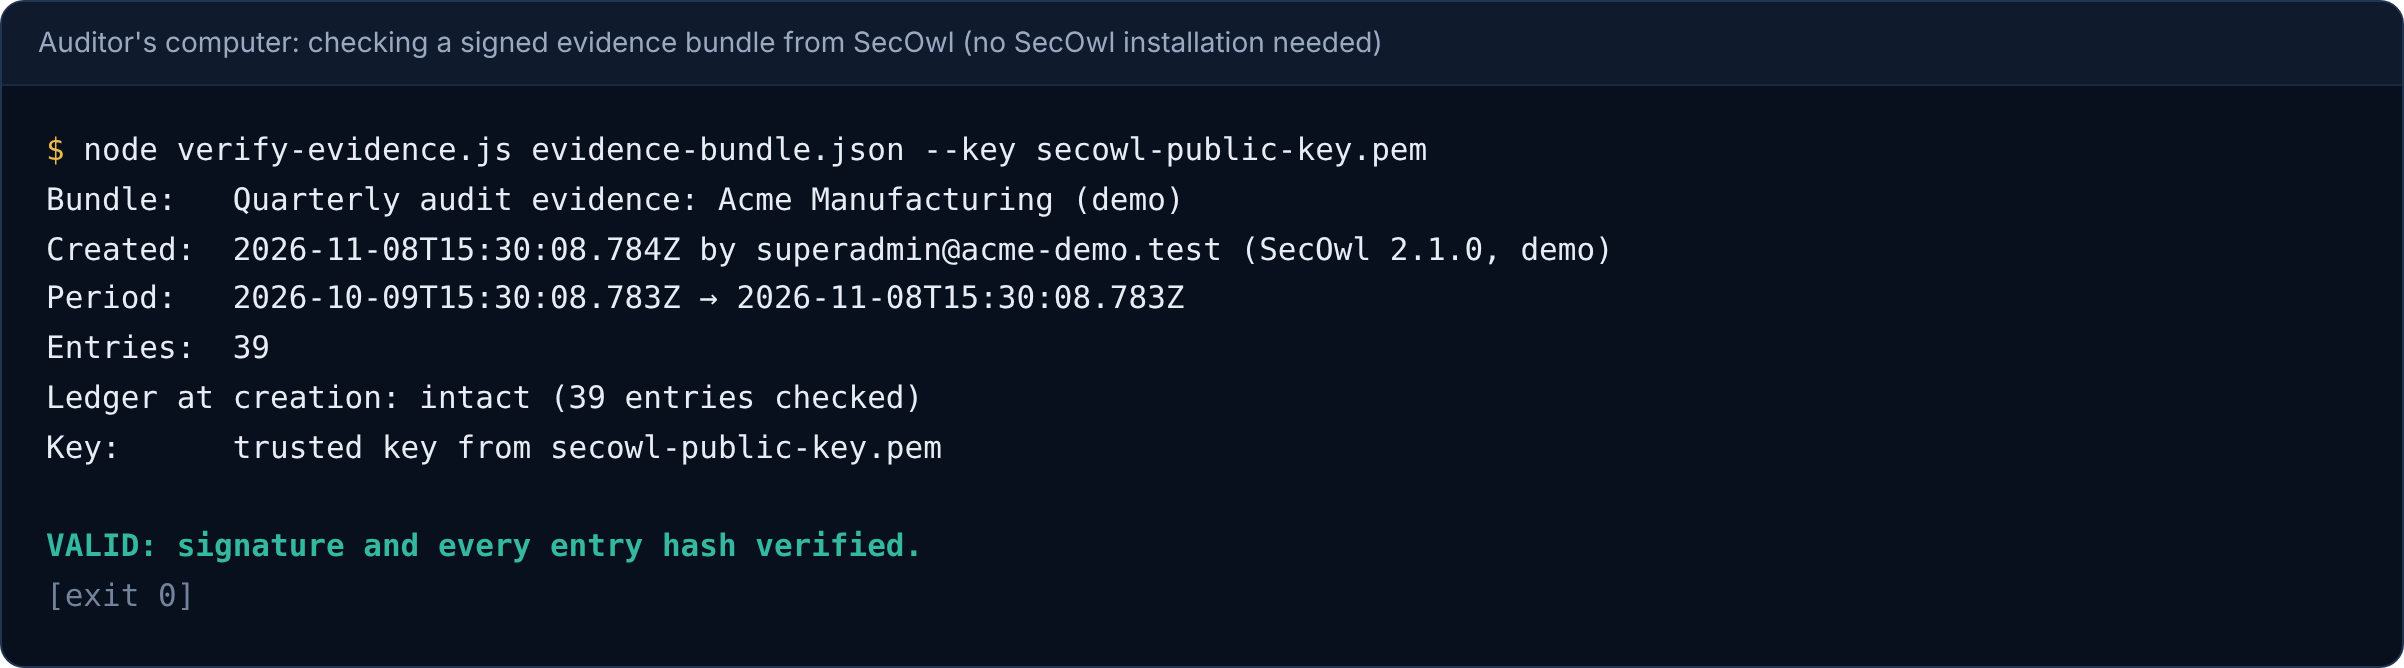
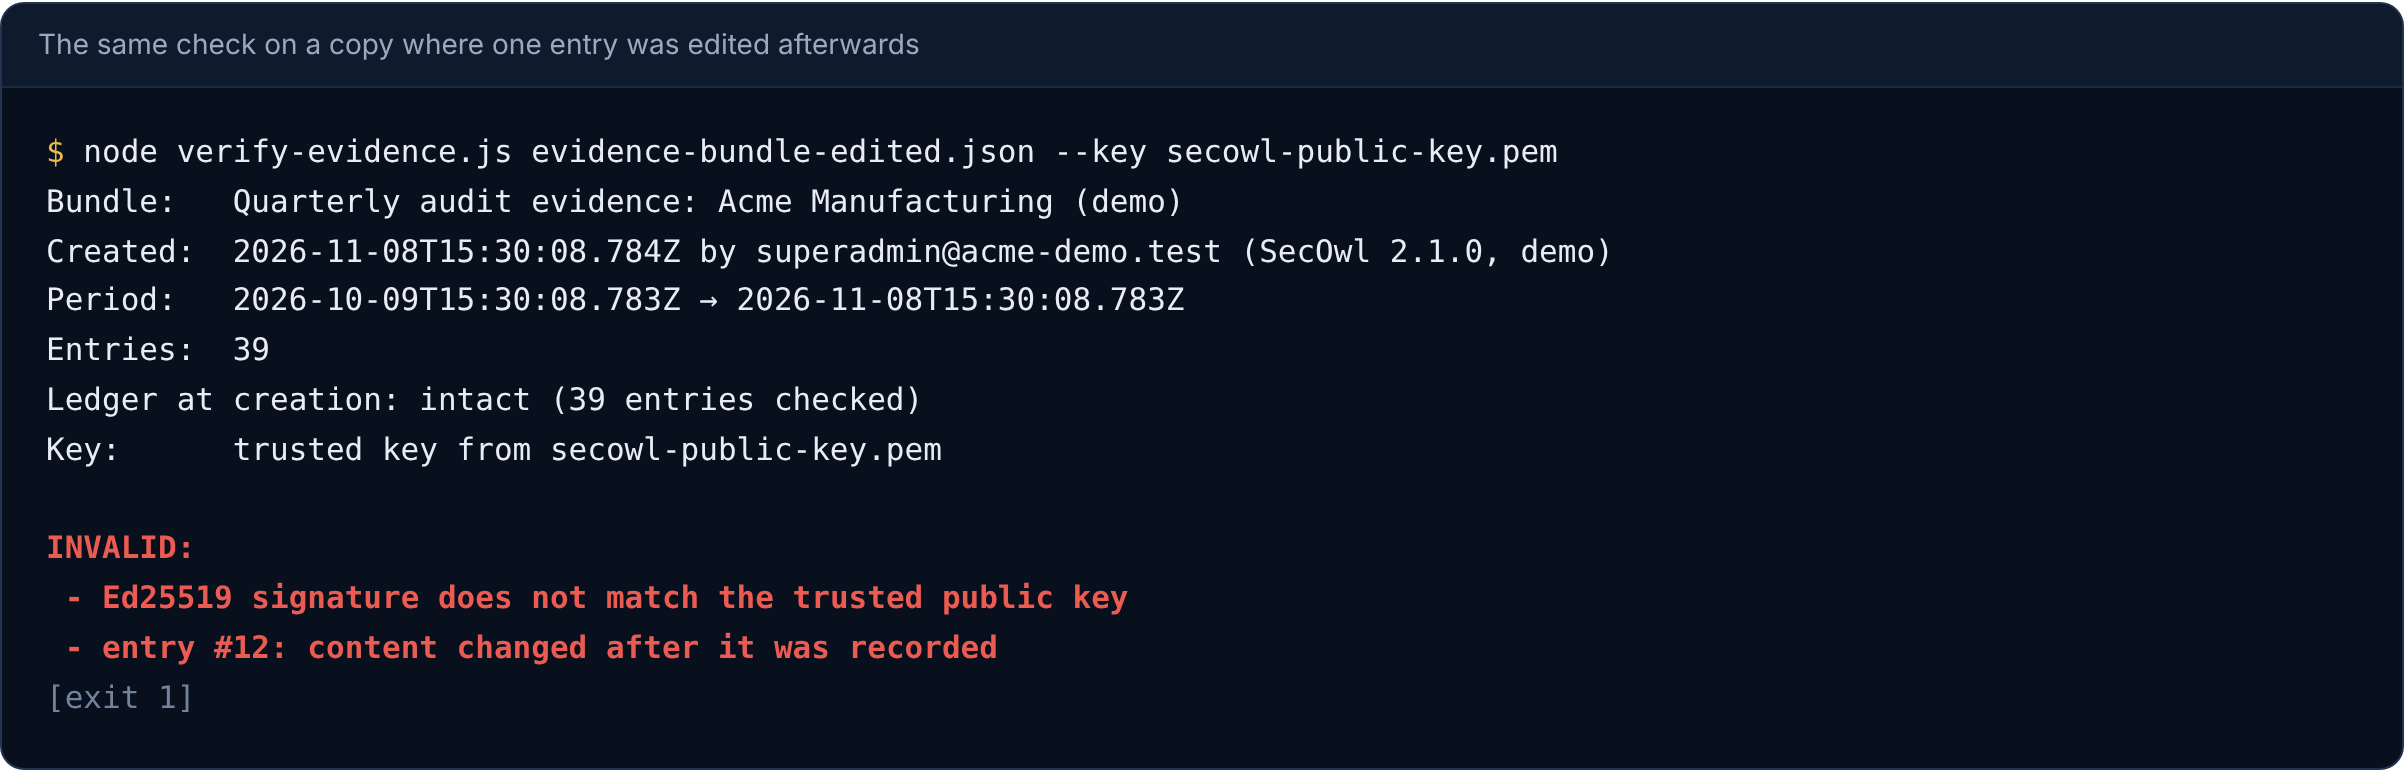
The key belongs to the demo installation used for these captures, so it proves the bundle came from that installation. In your own deployment, get the trusted key from your SecOwl administrator through a separate channel.
Automated tests
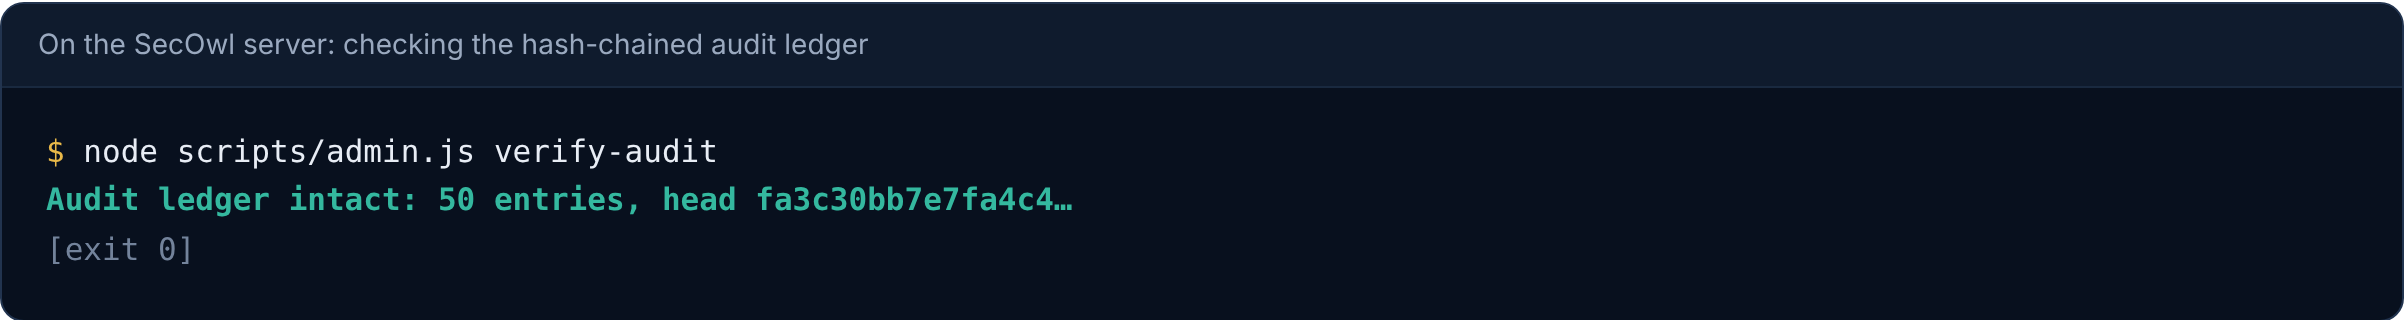
Reports
Every report is stored with its SHA-256 fingerprint so a copy can be checked later. Download the PDFs generated for the demo company.
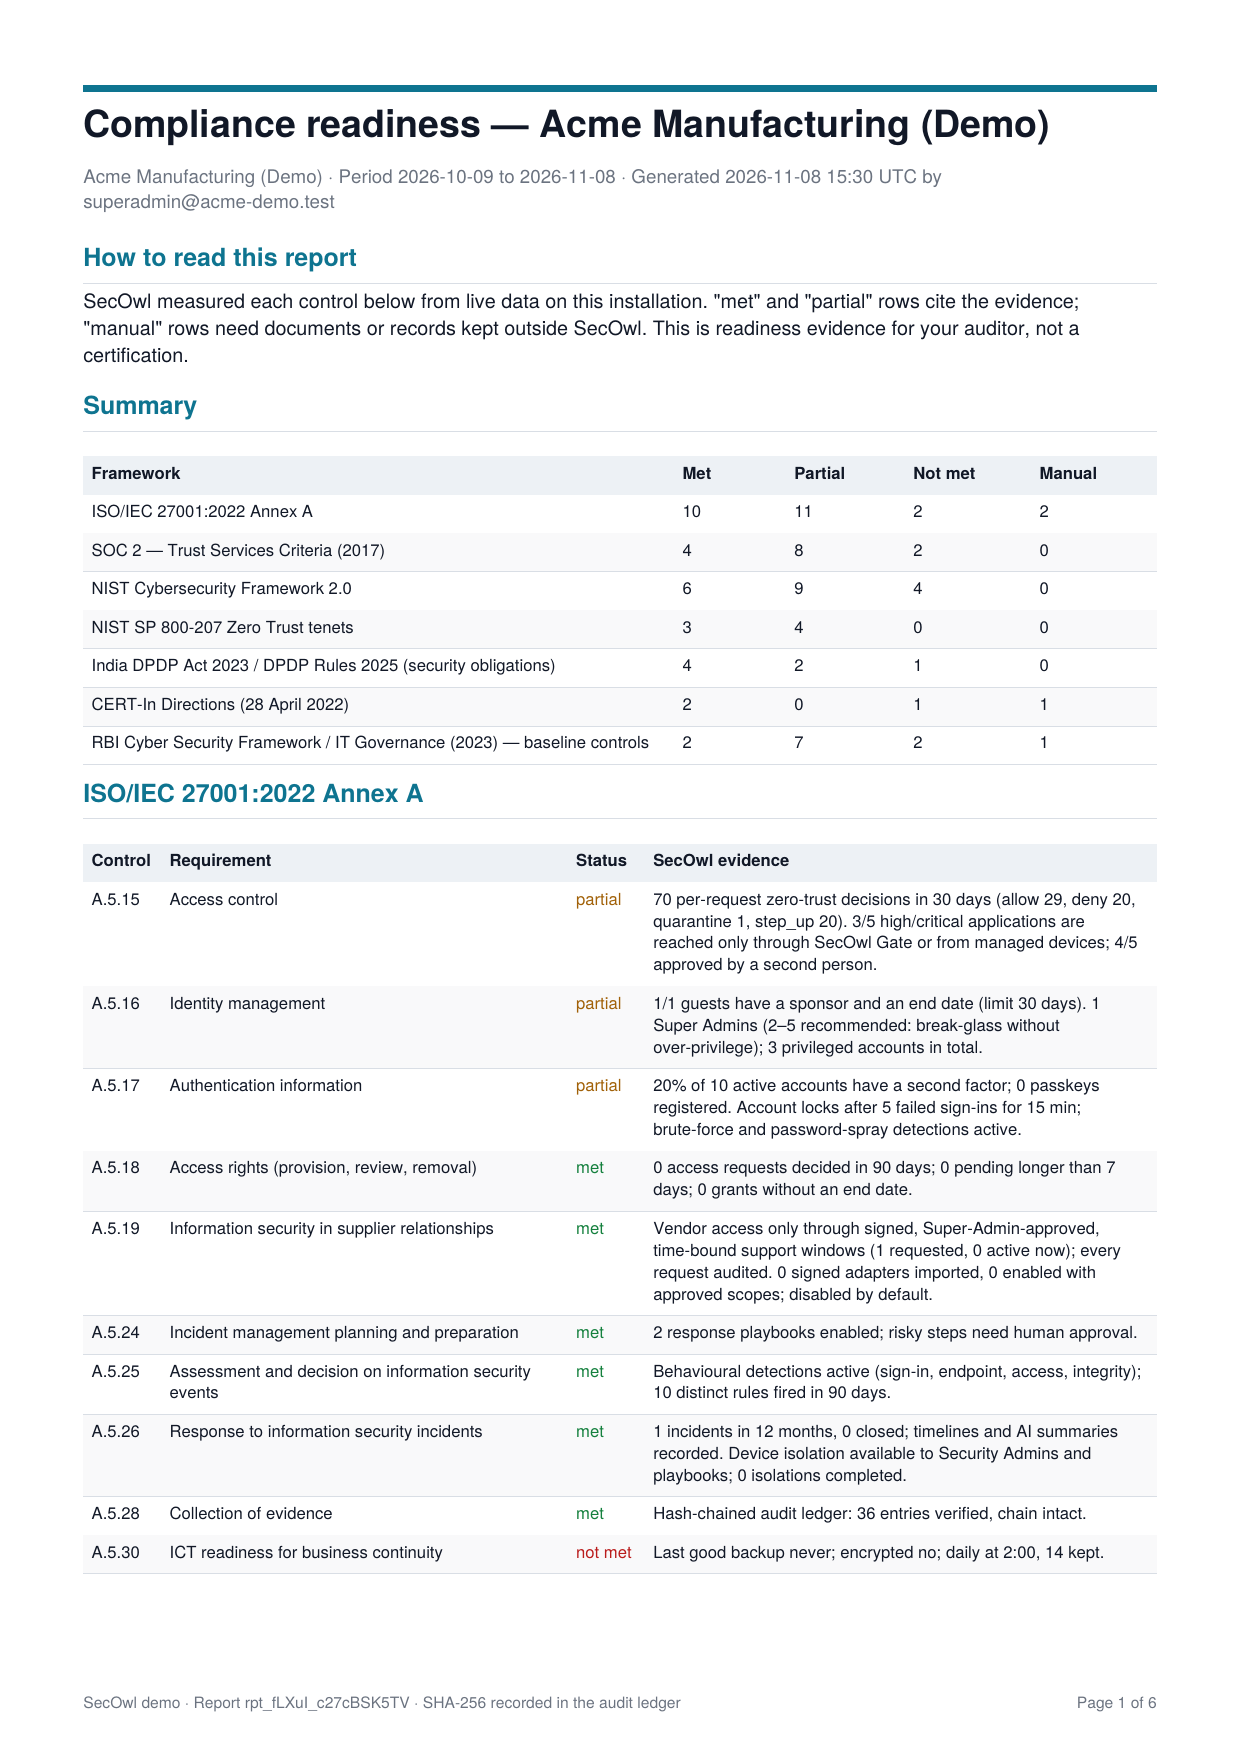
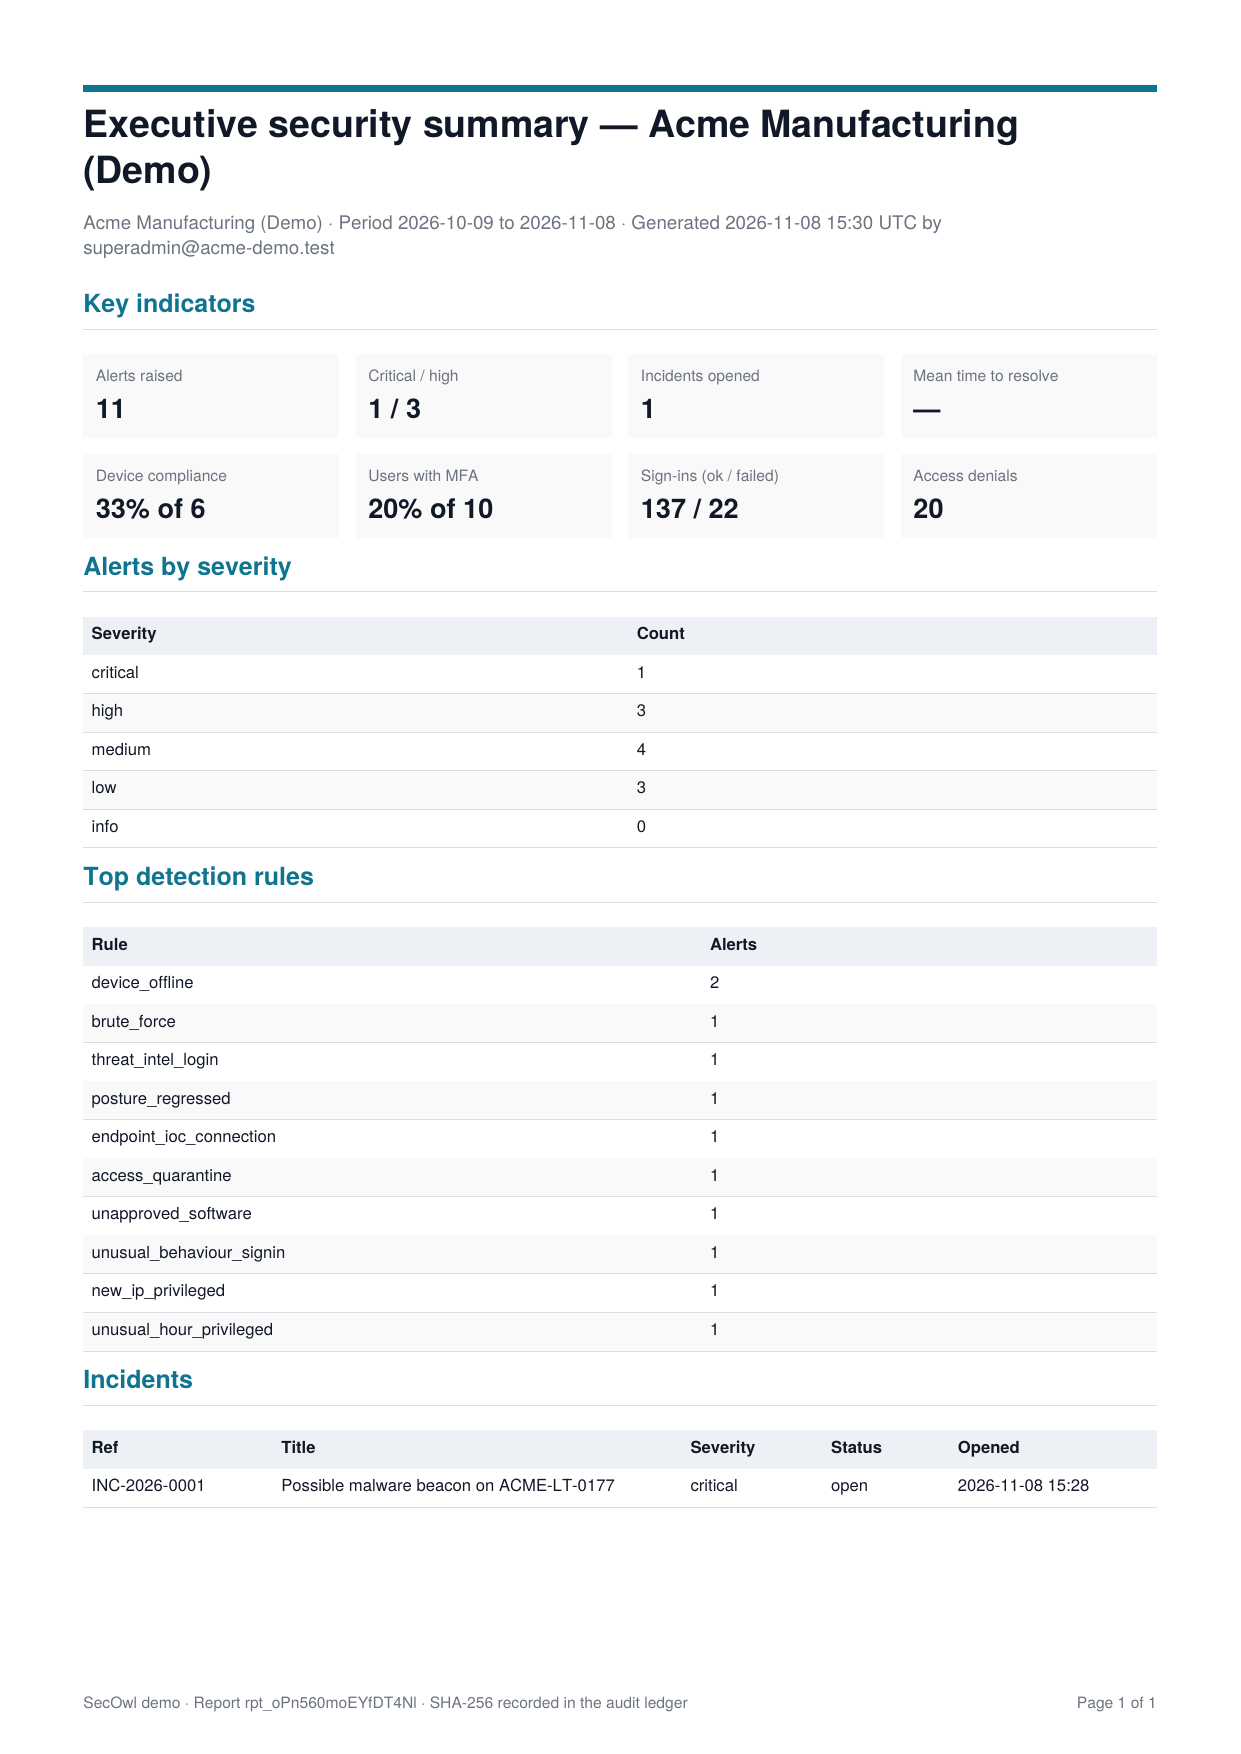
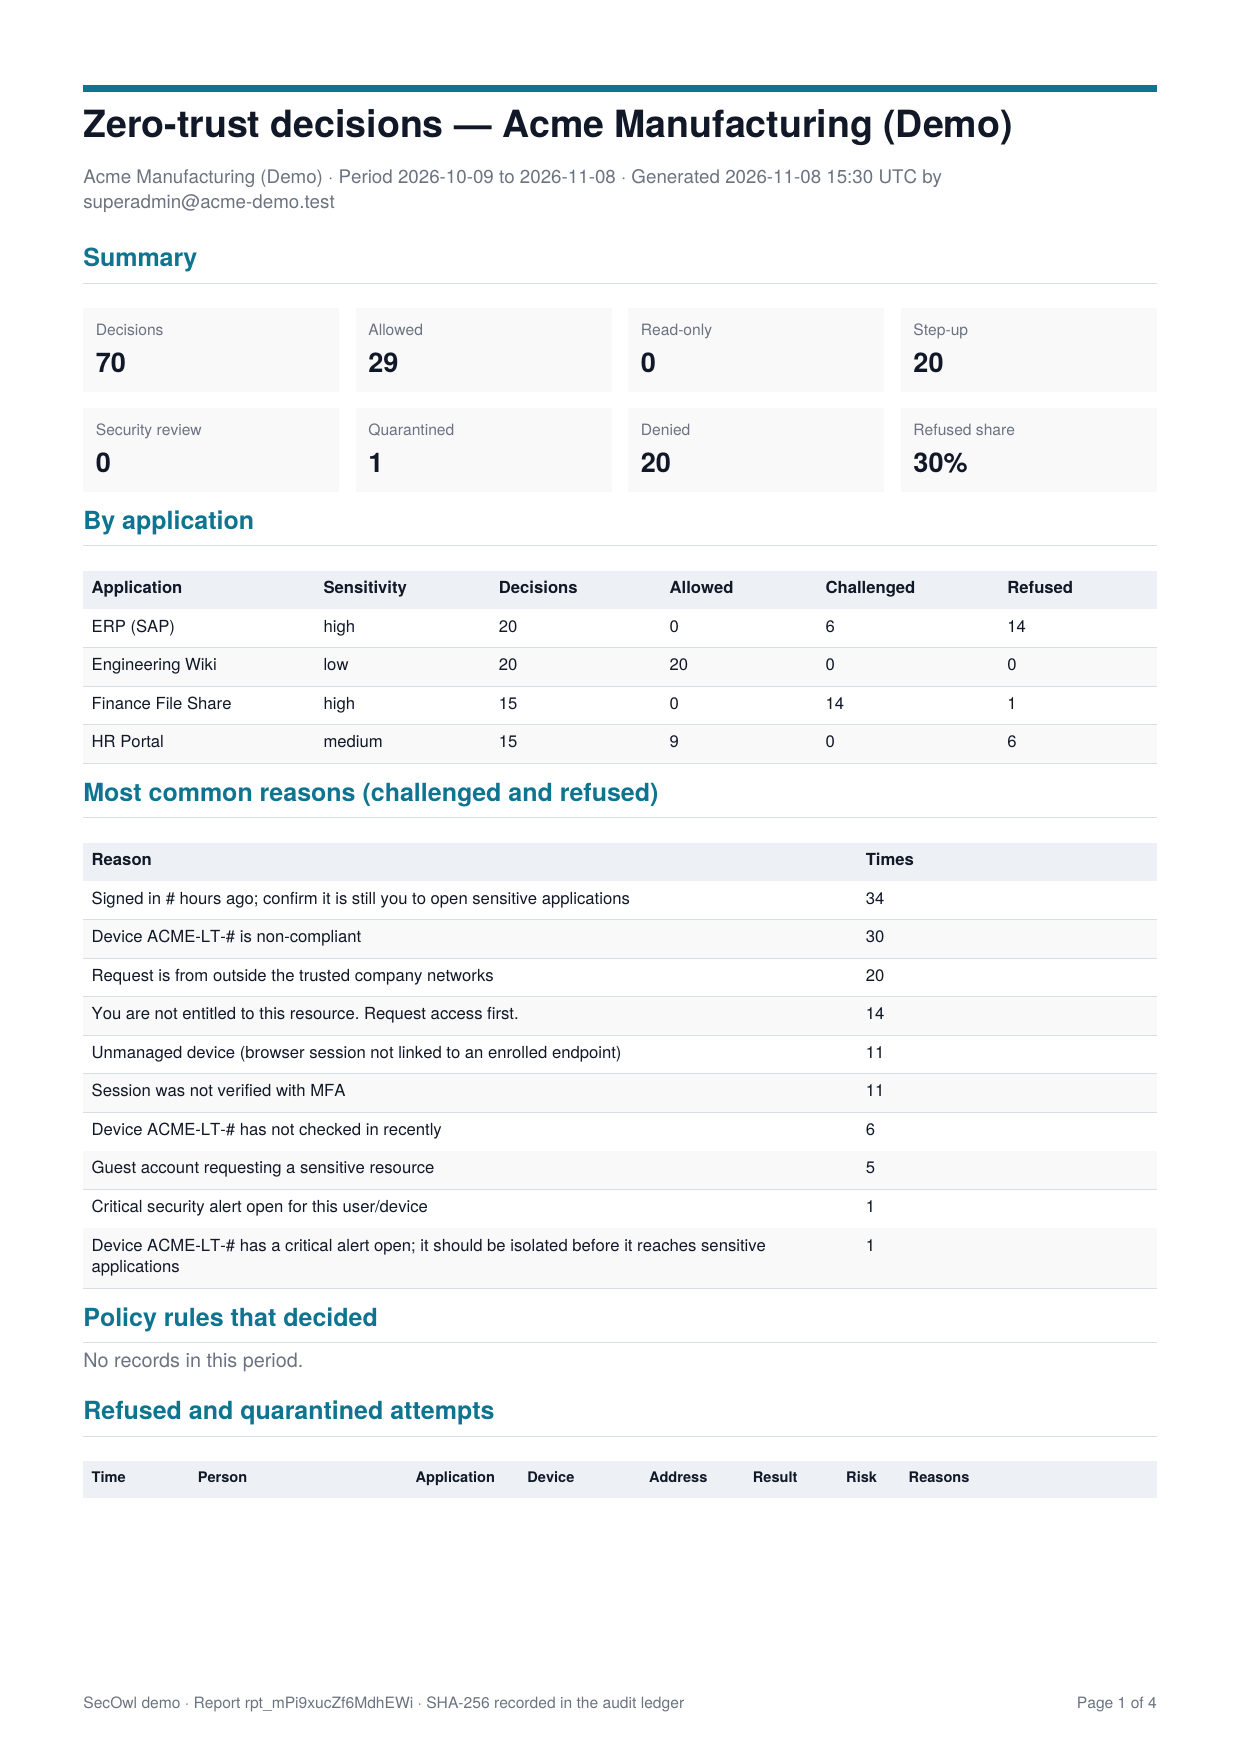
More evidence screens
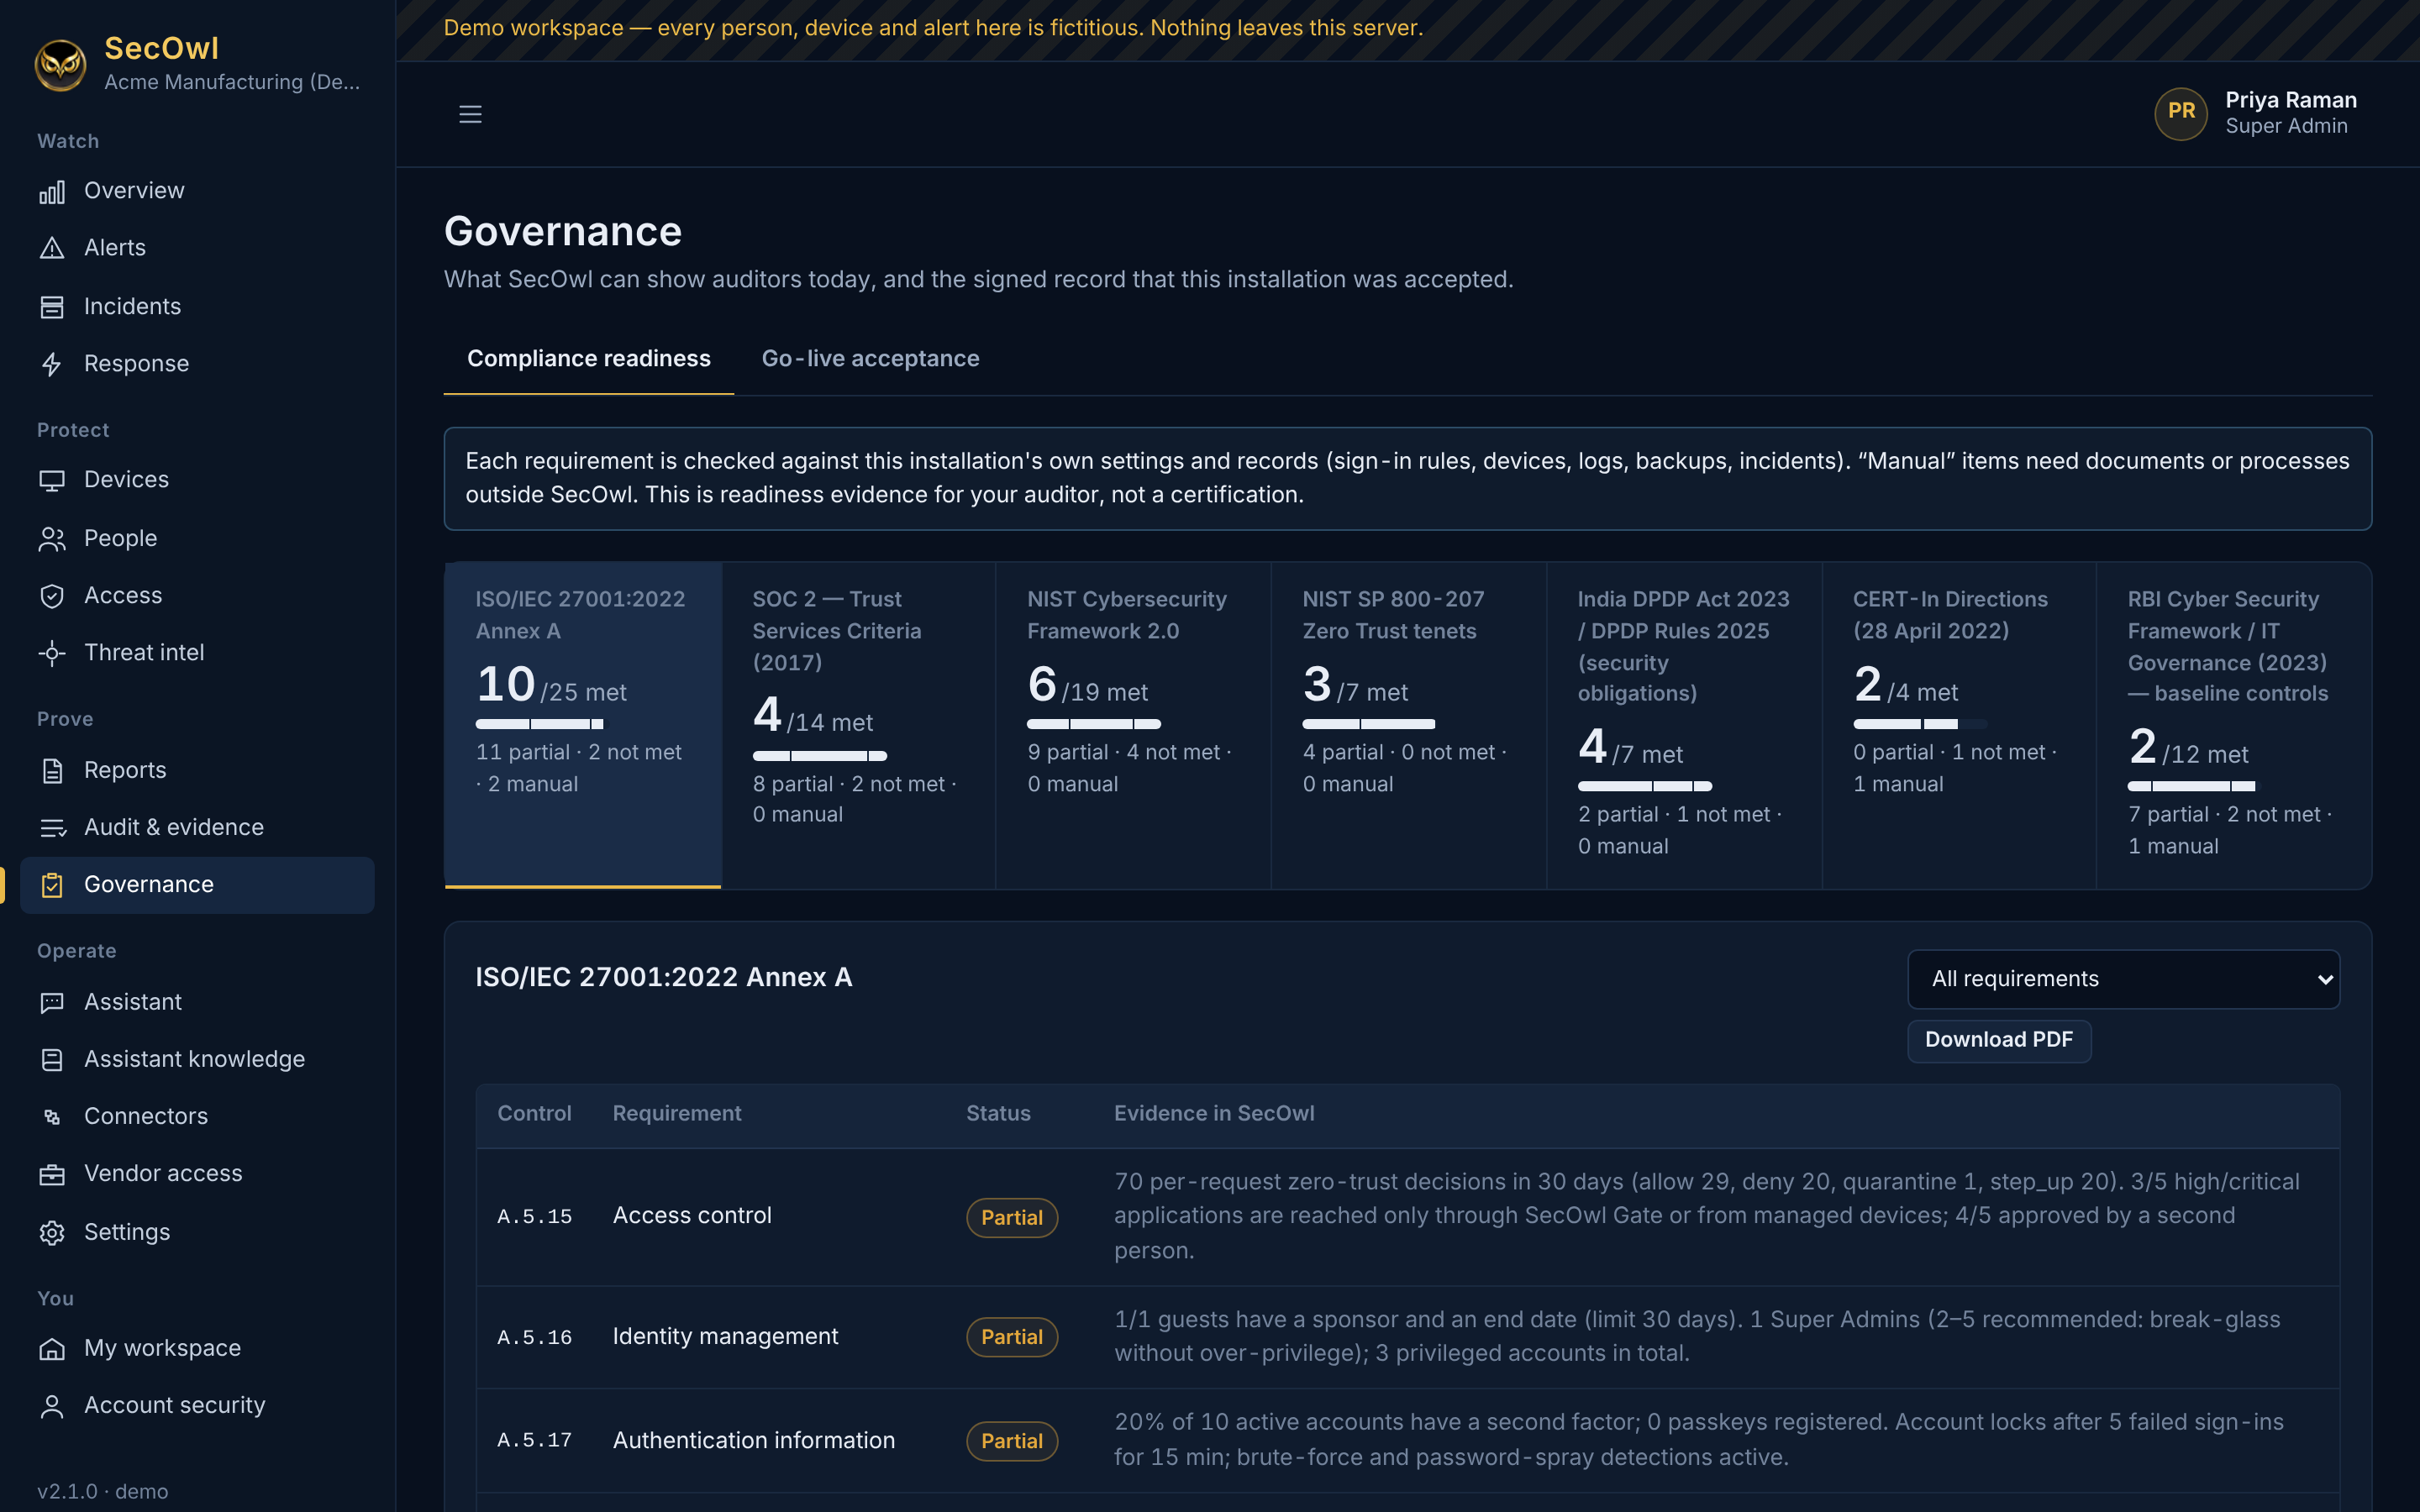
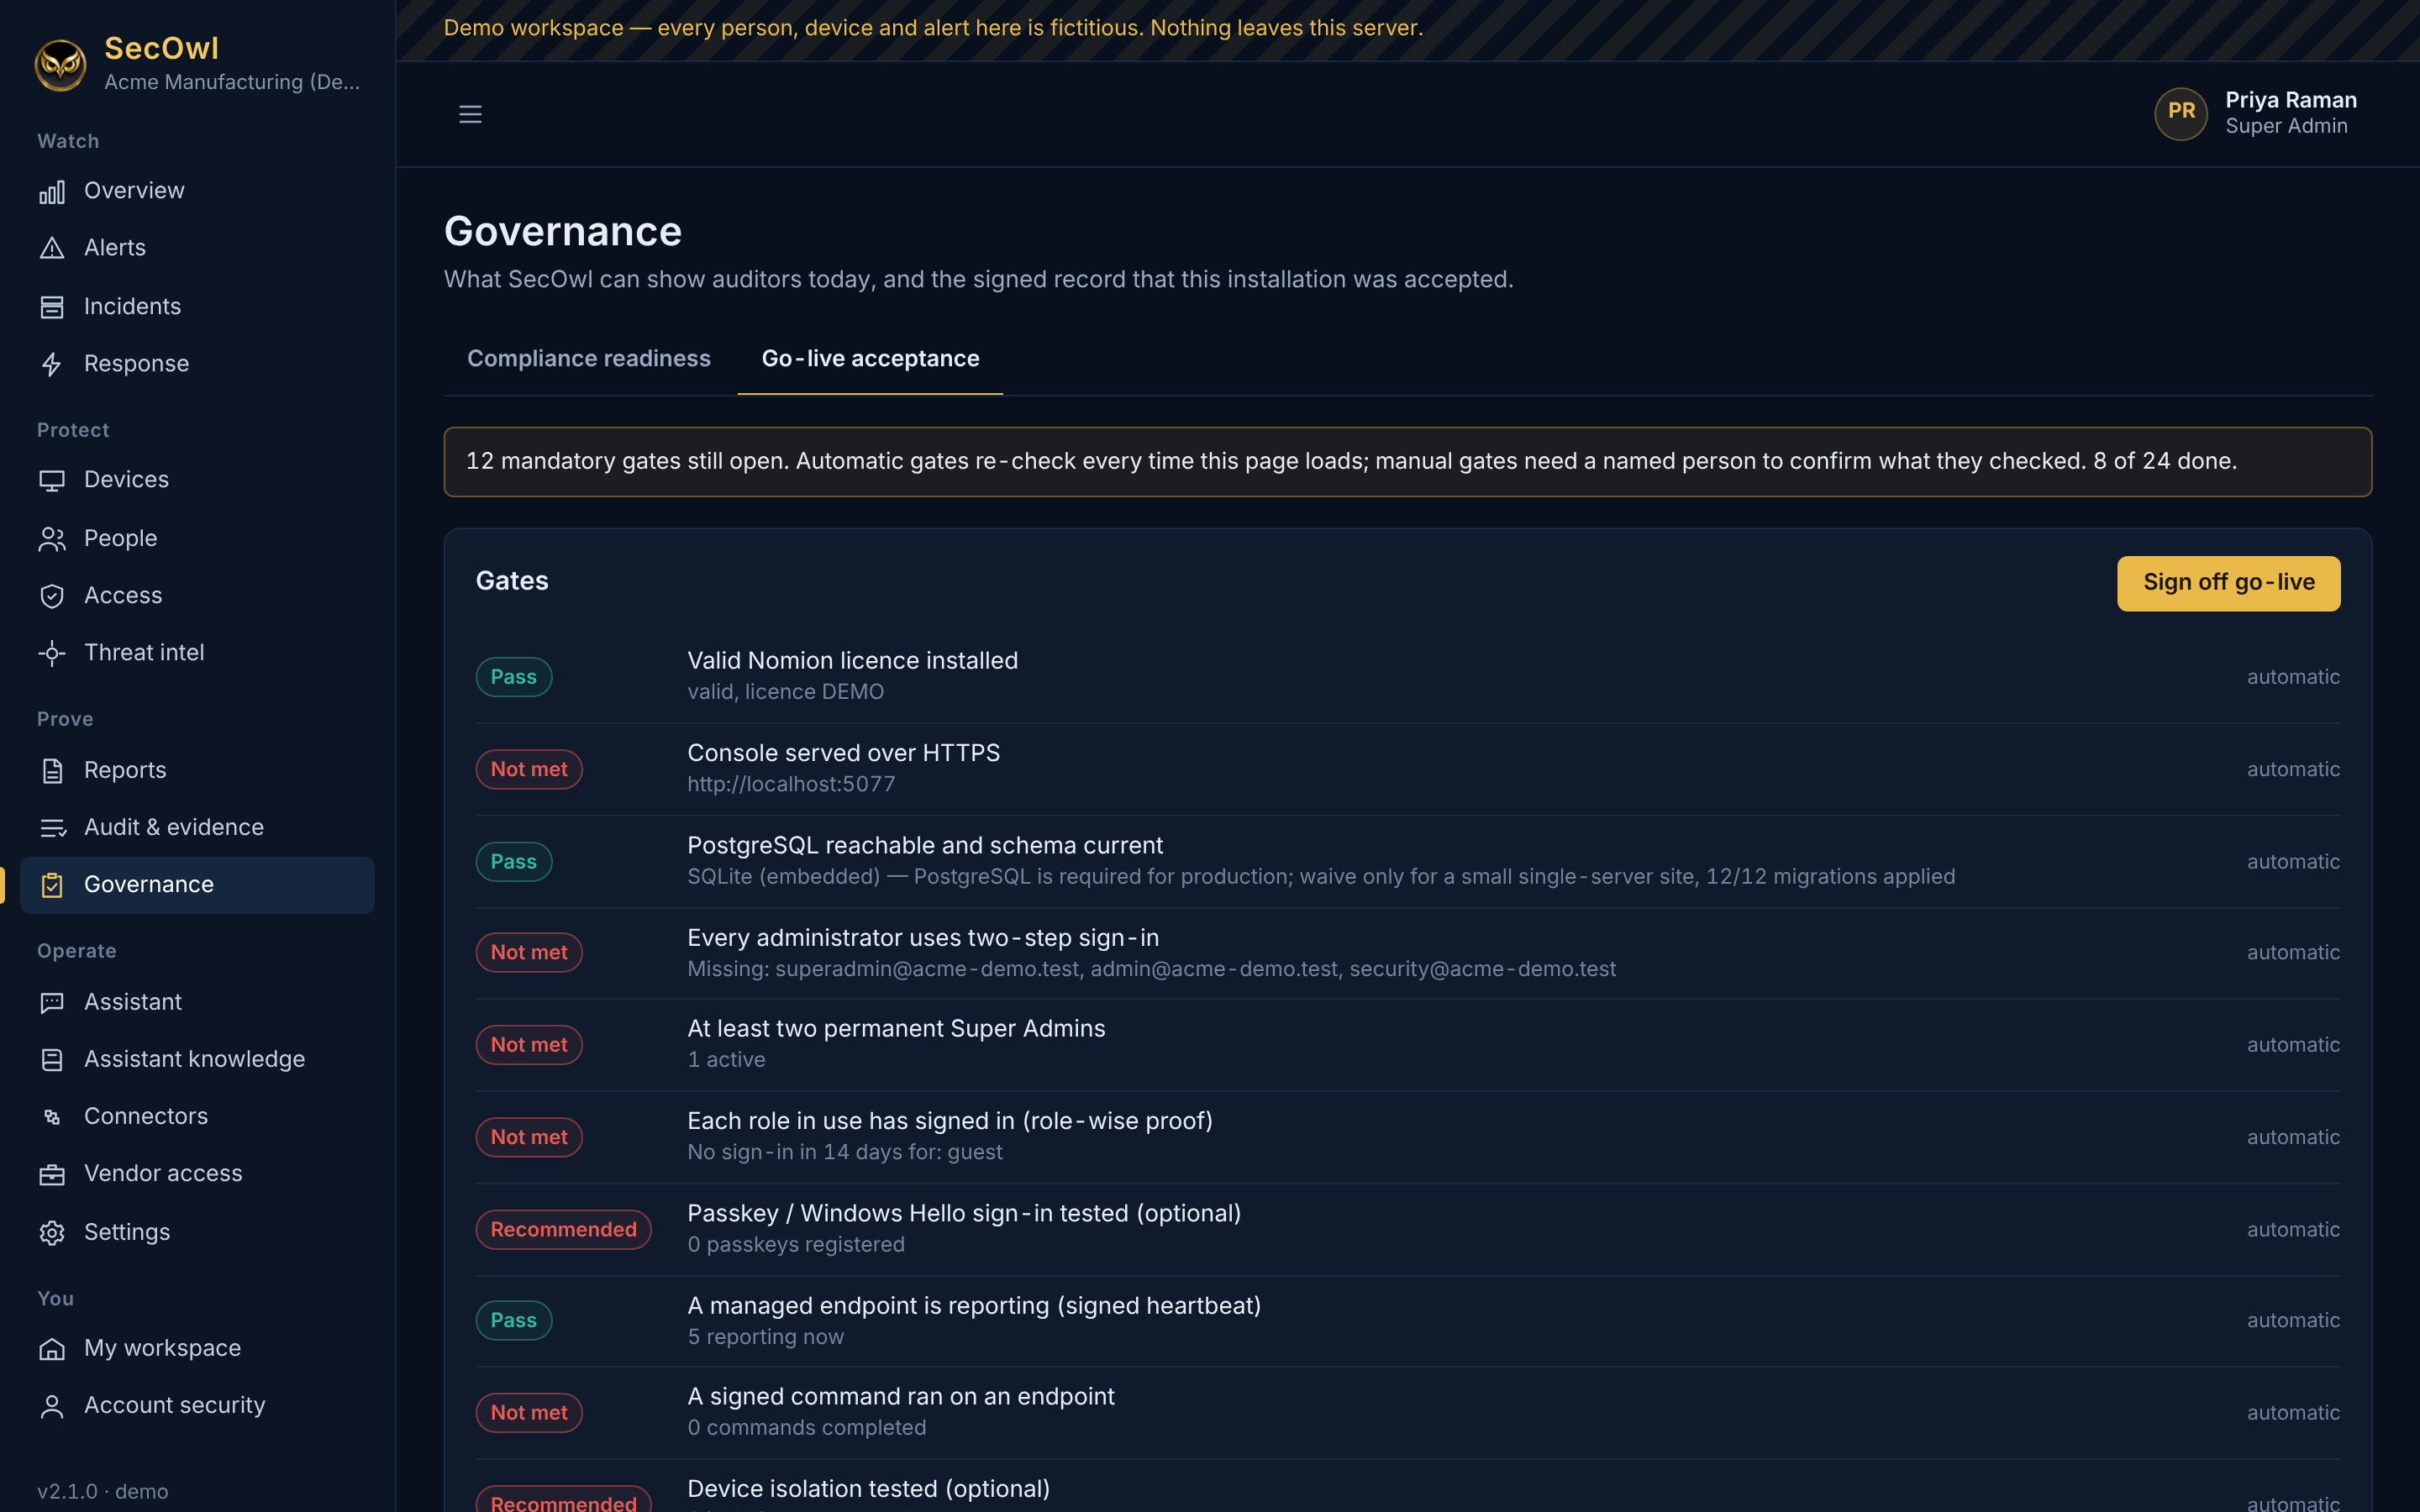
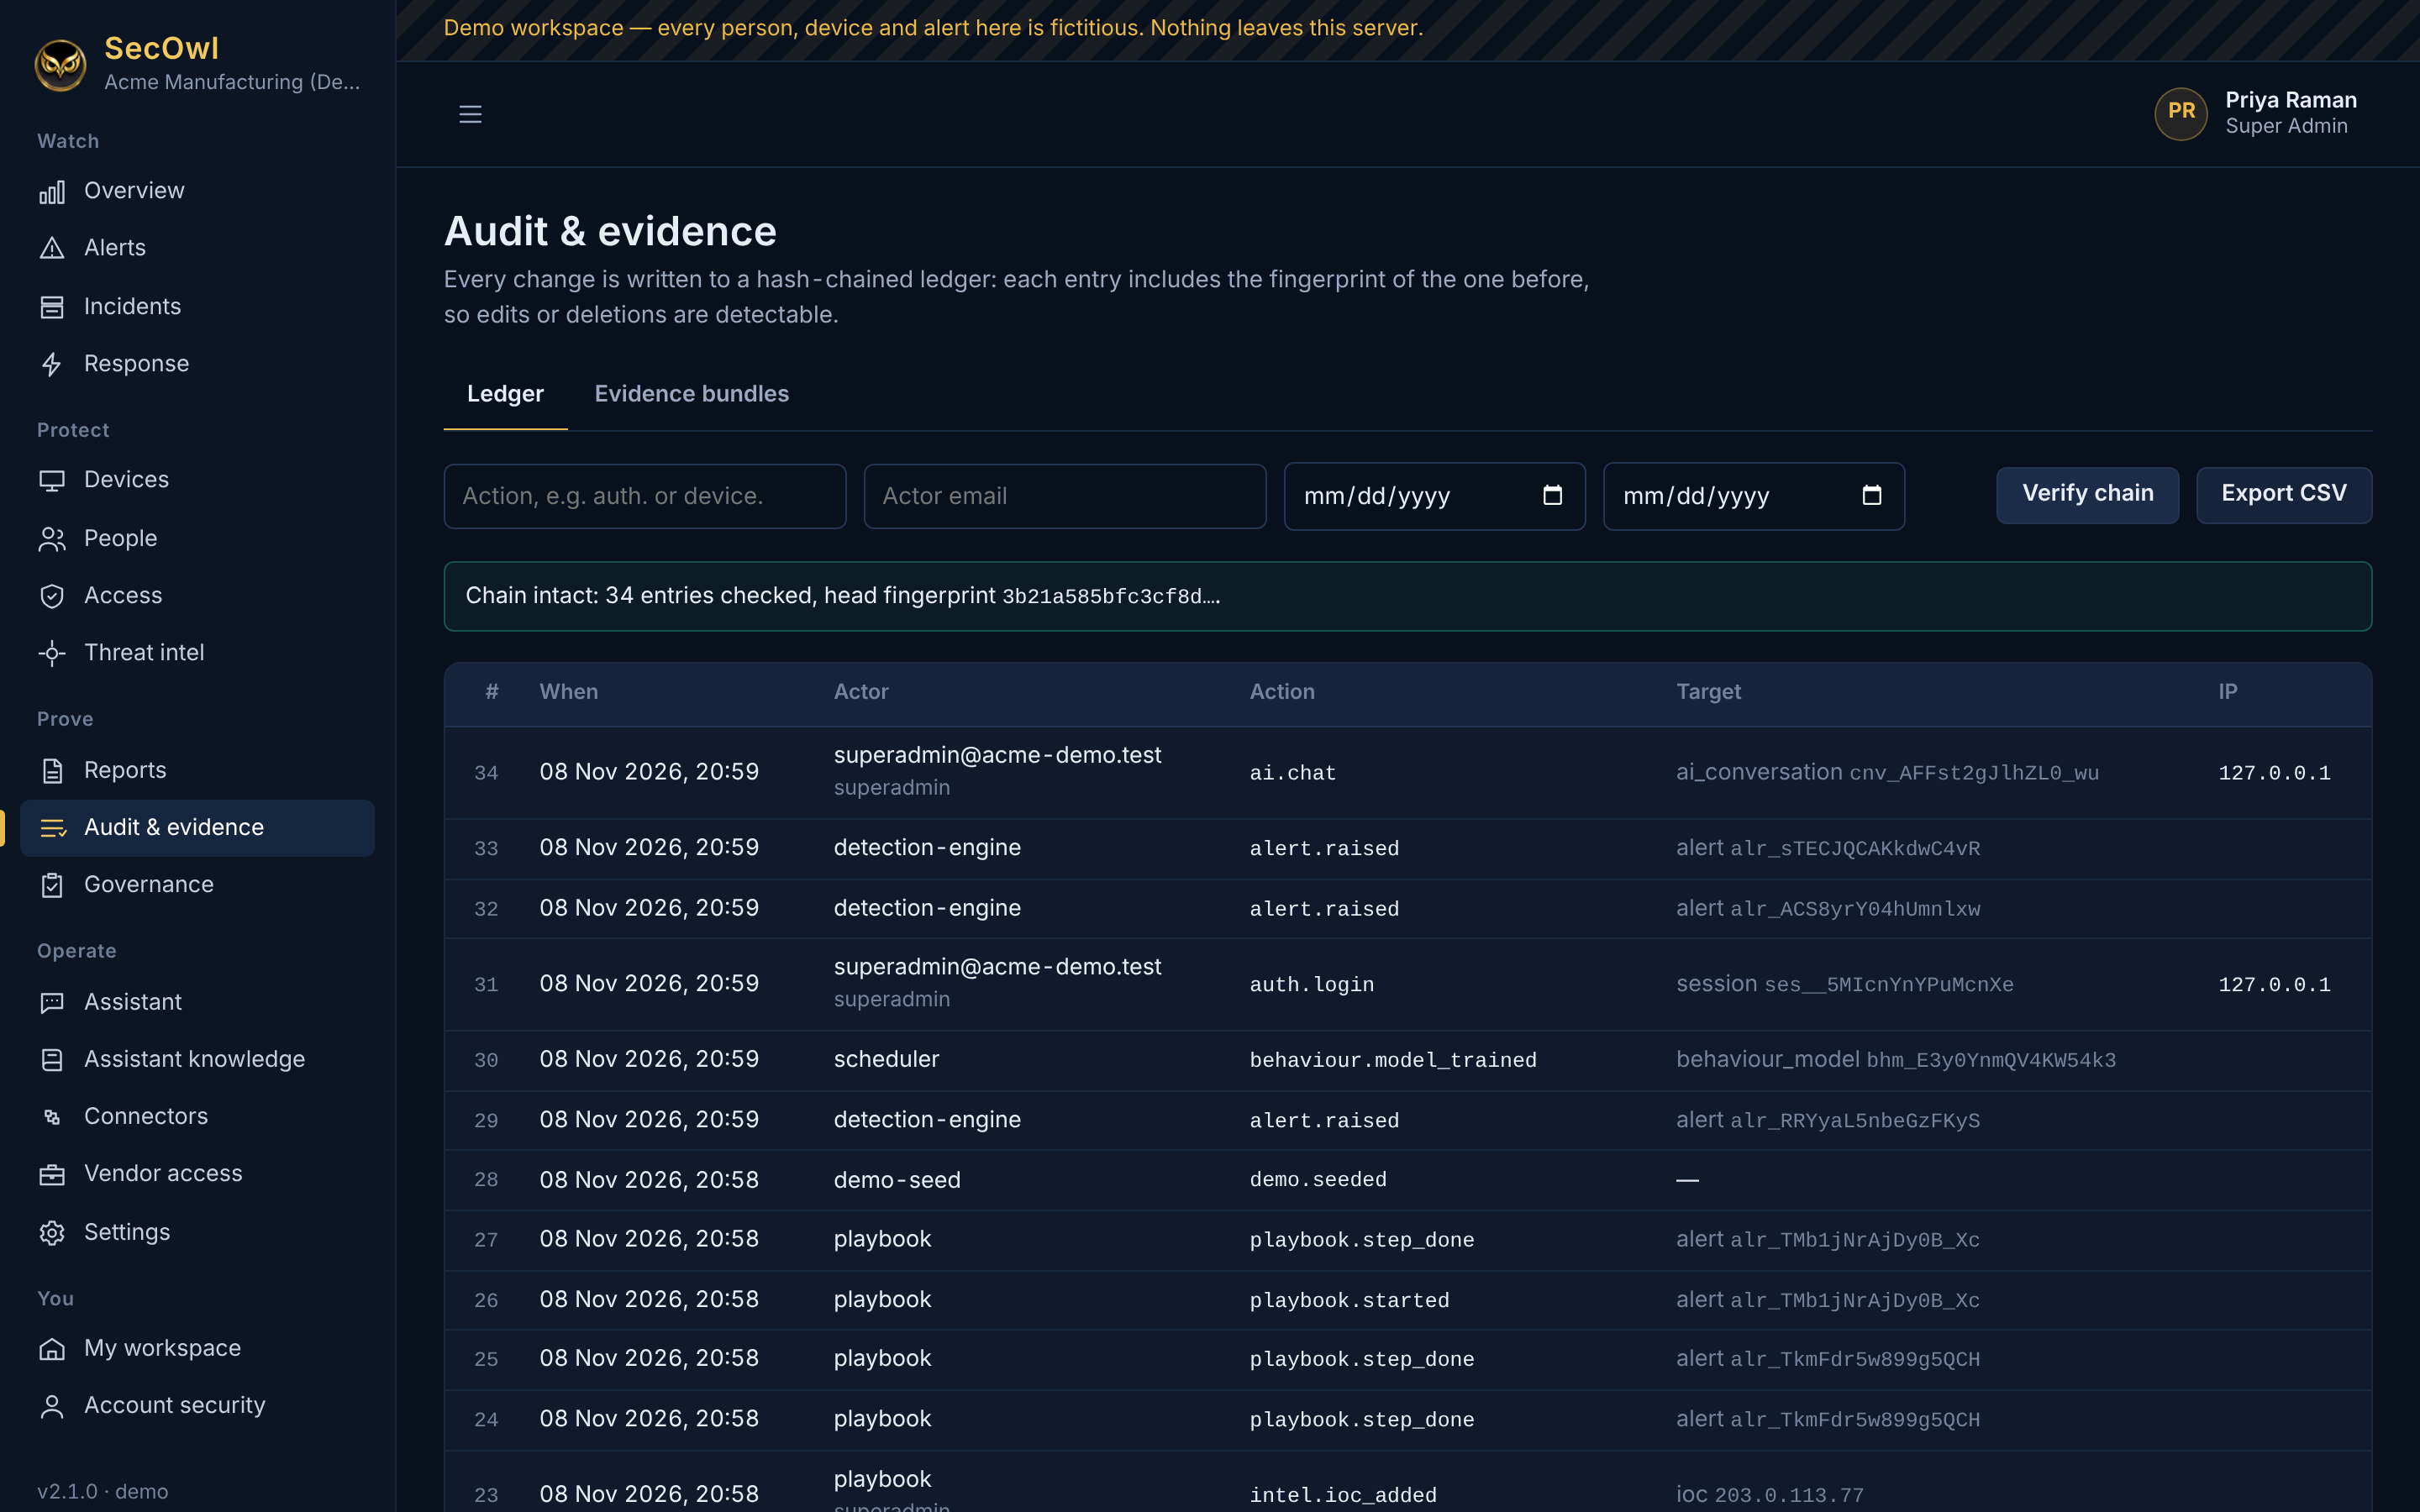
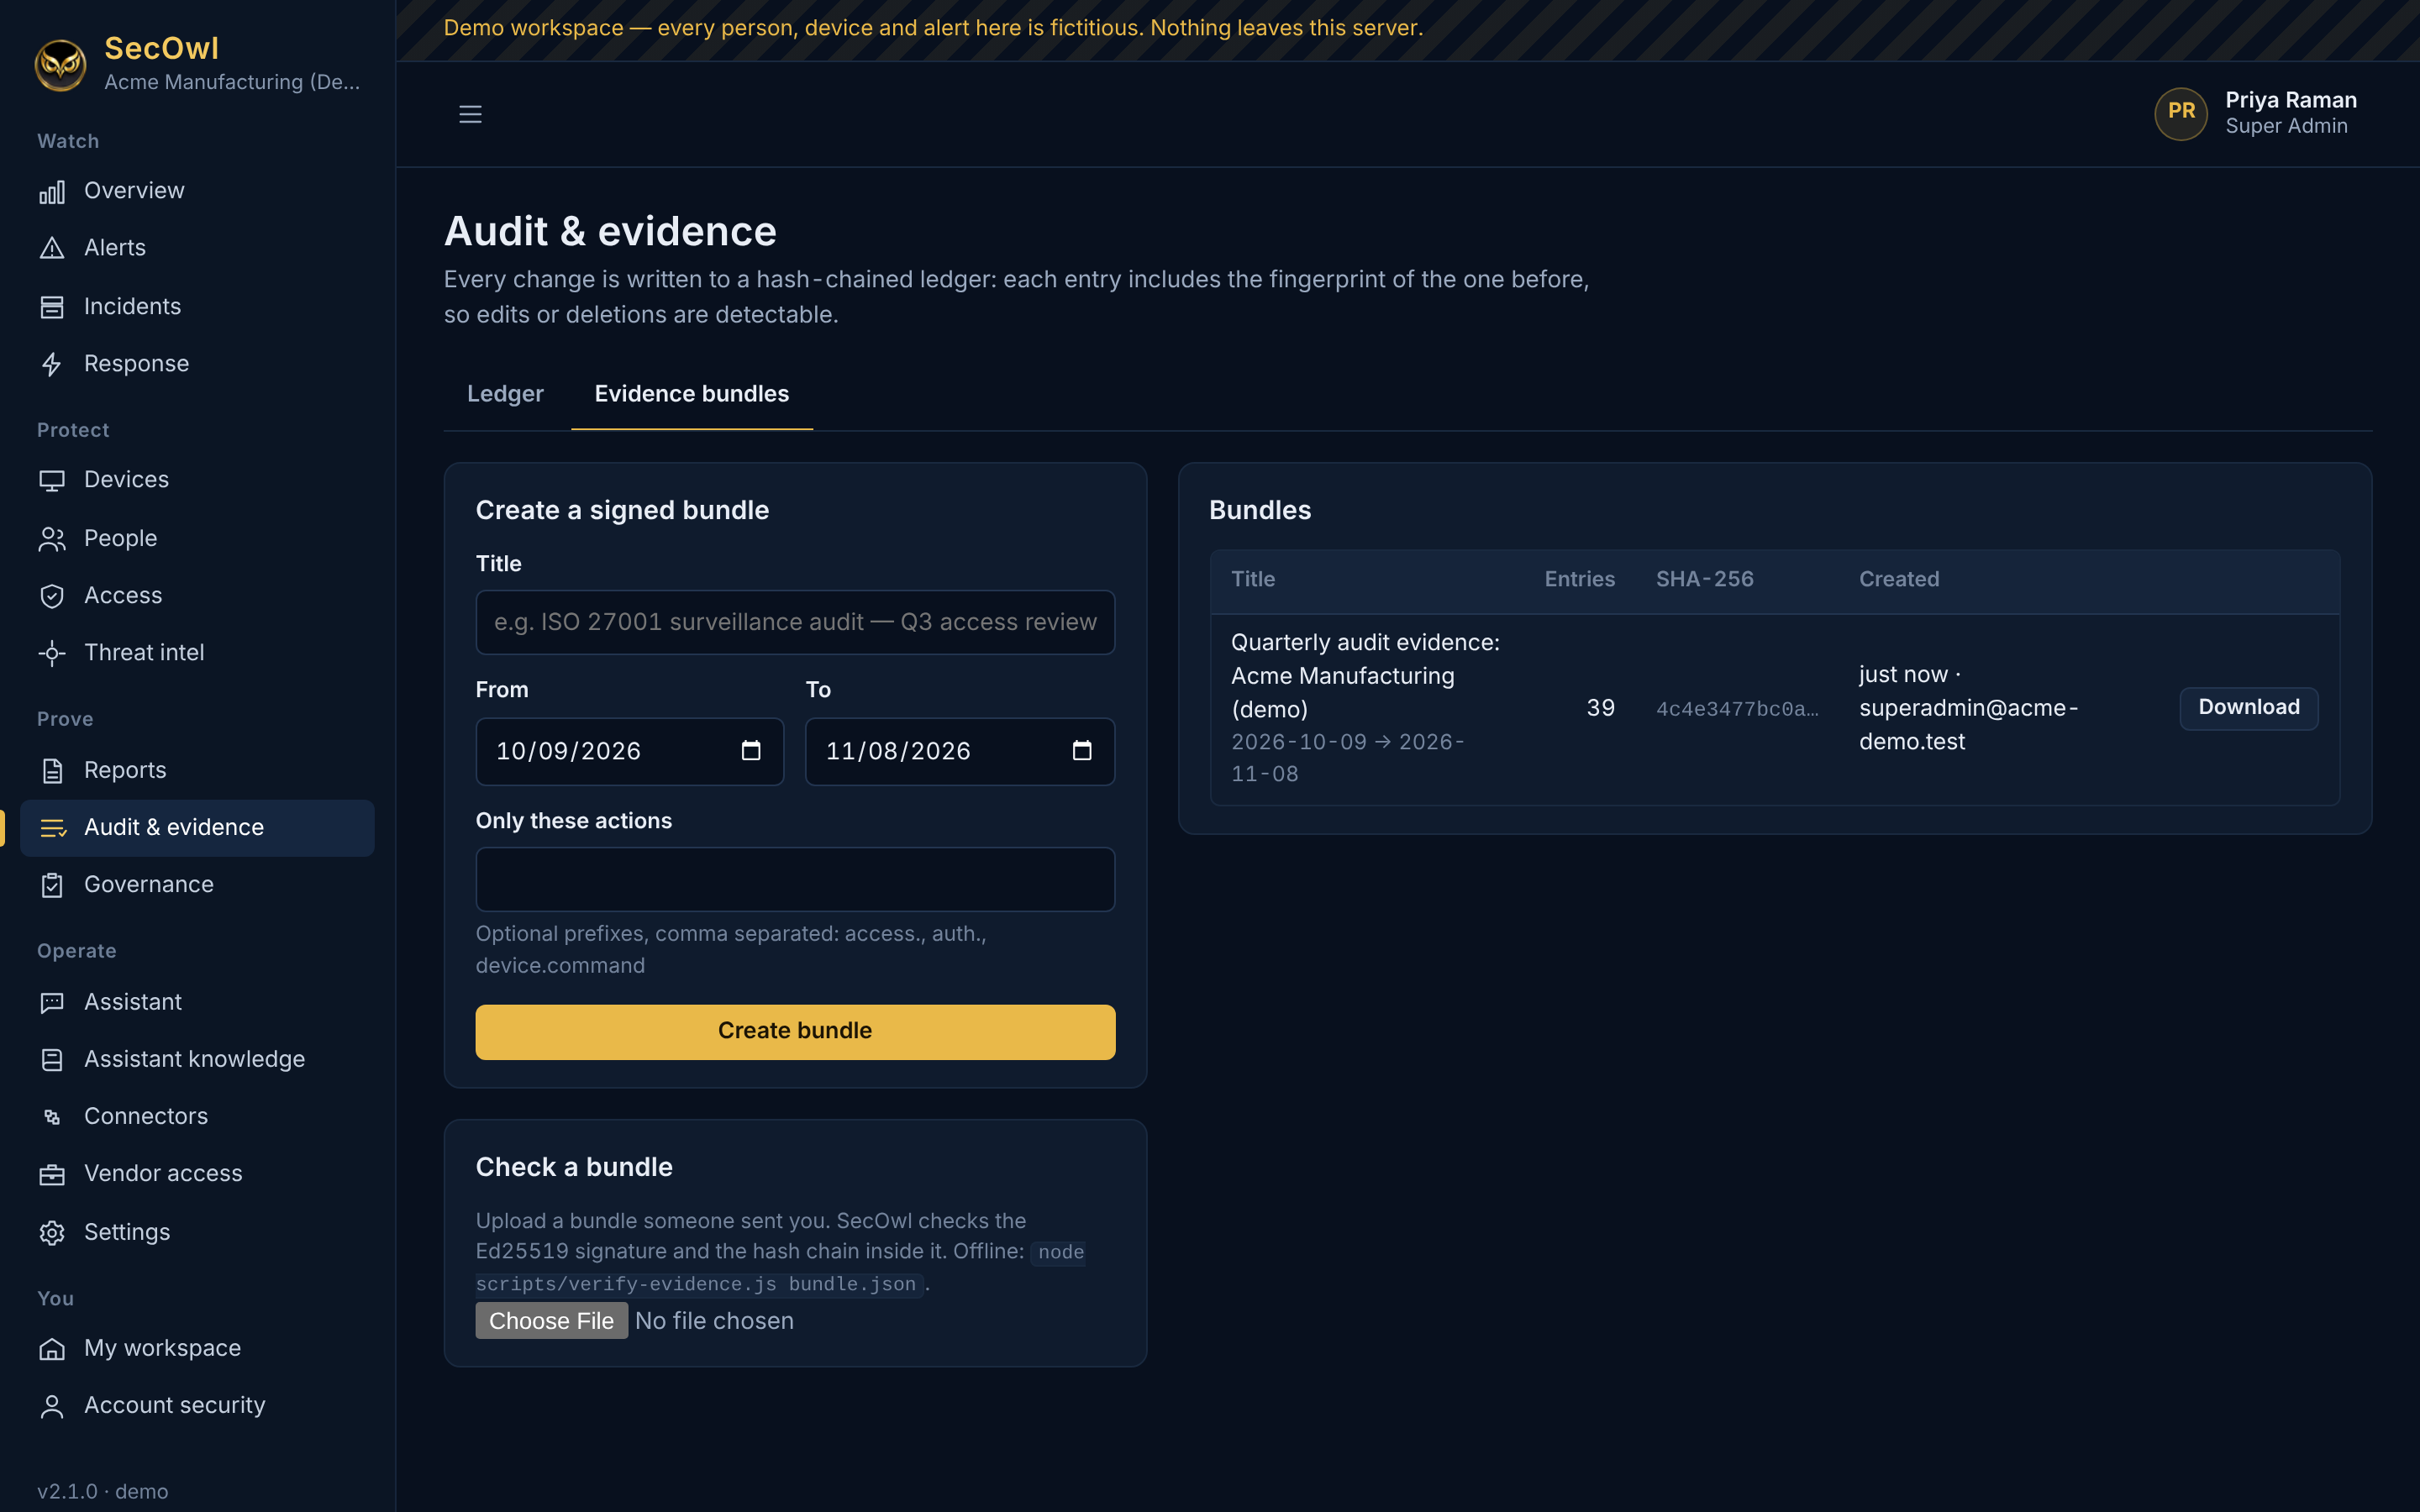
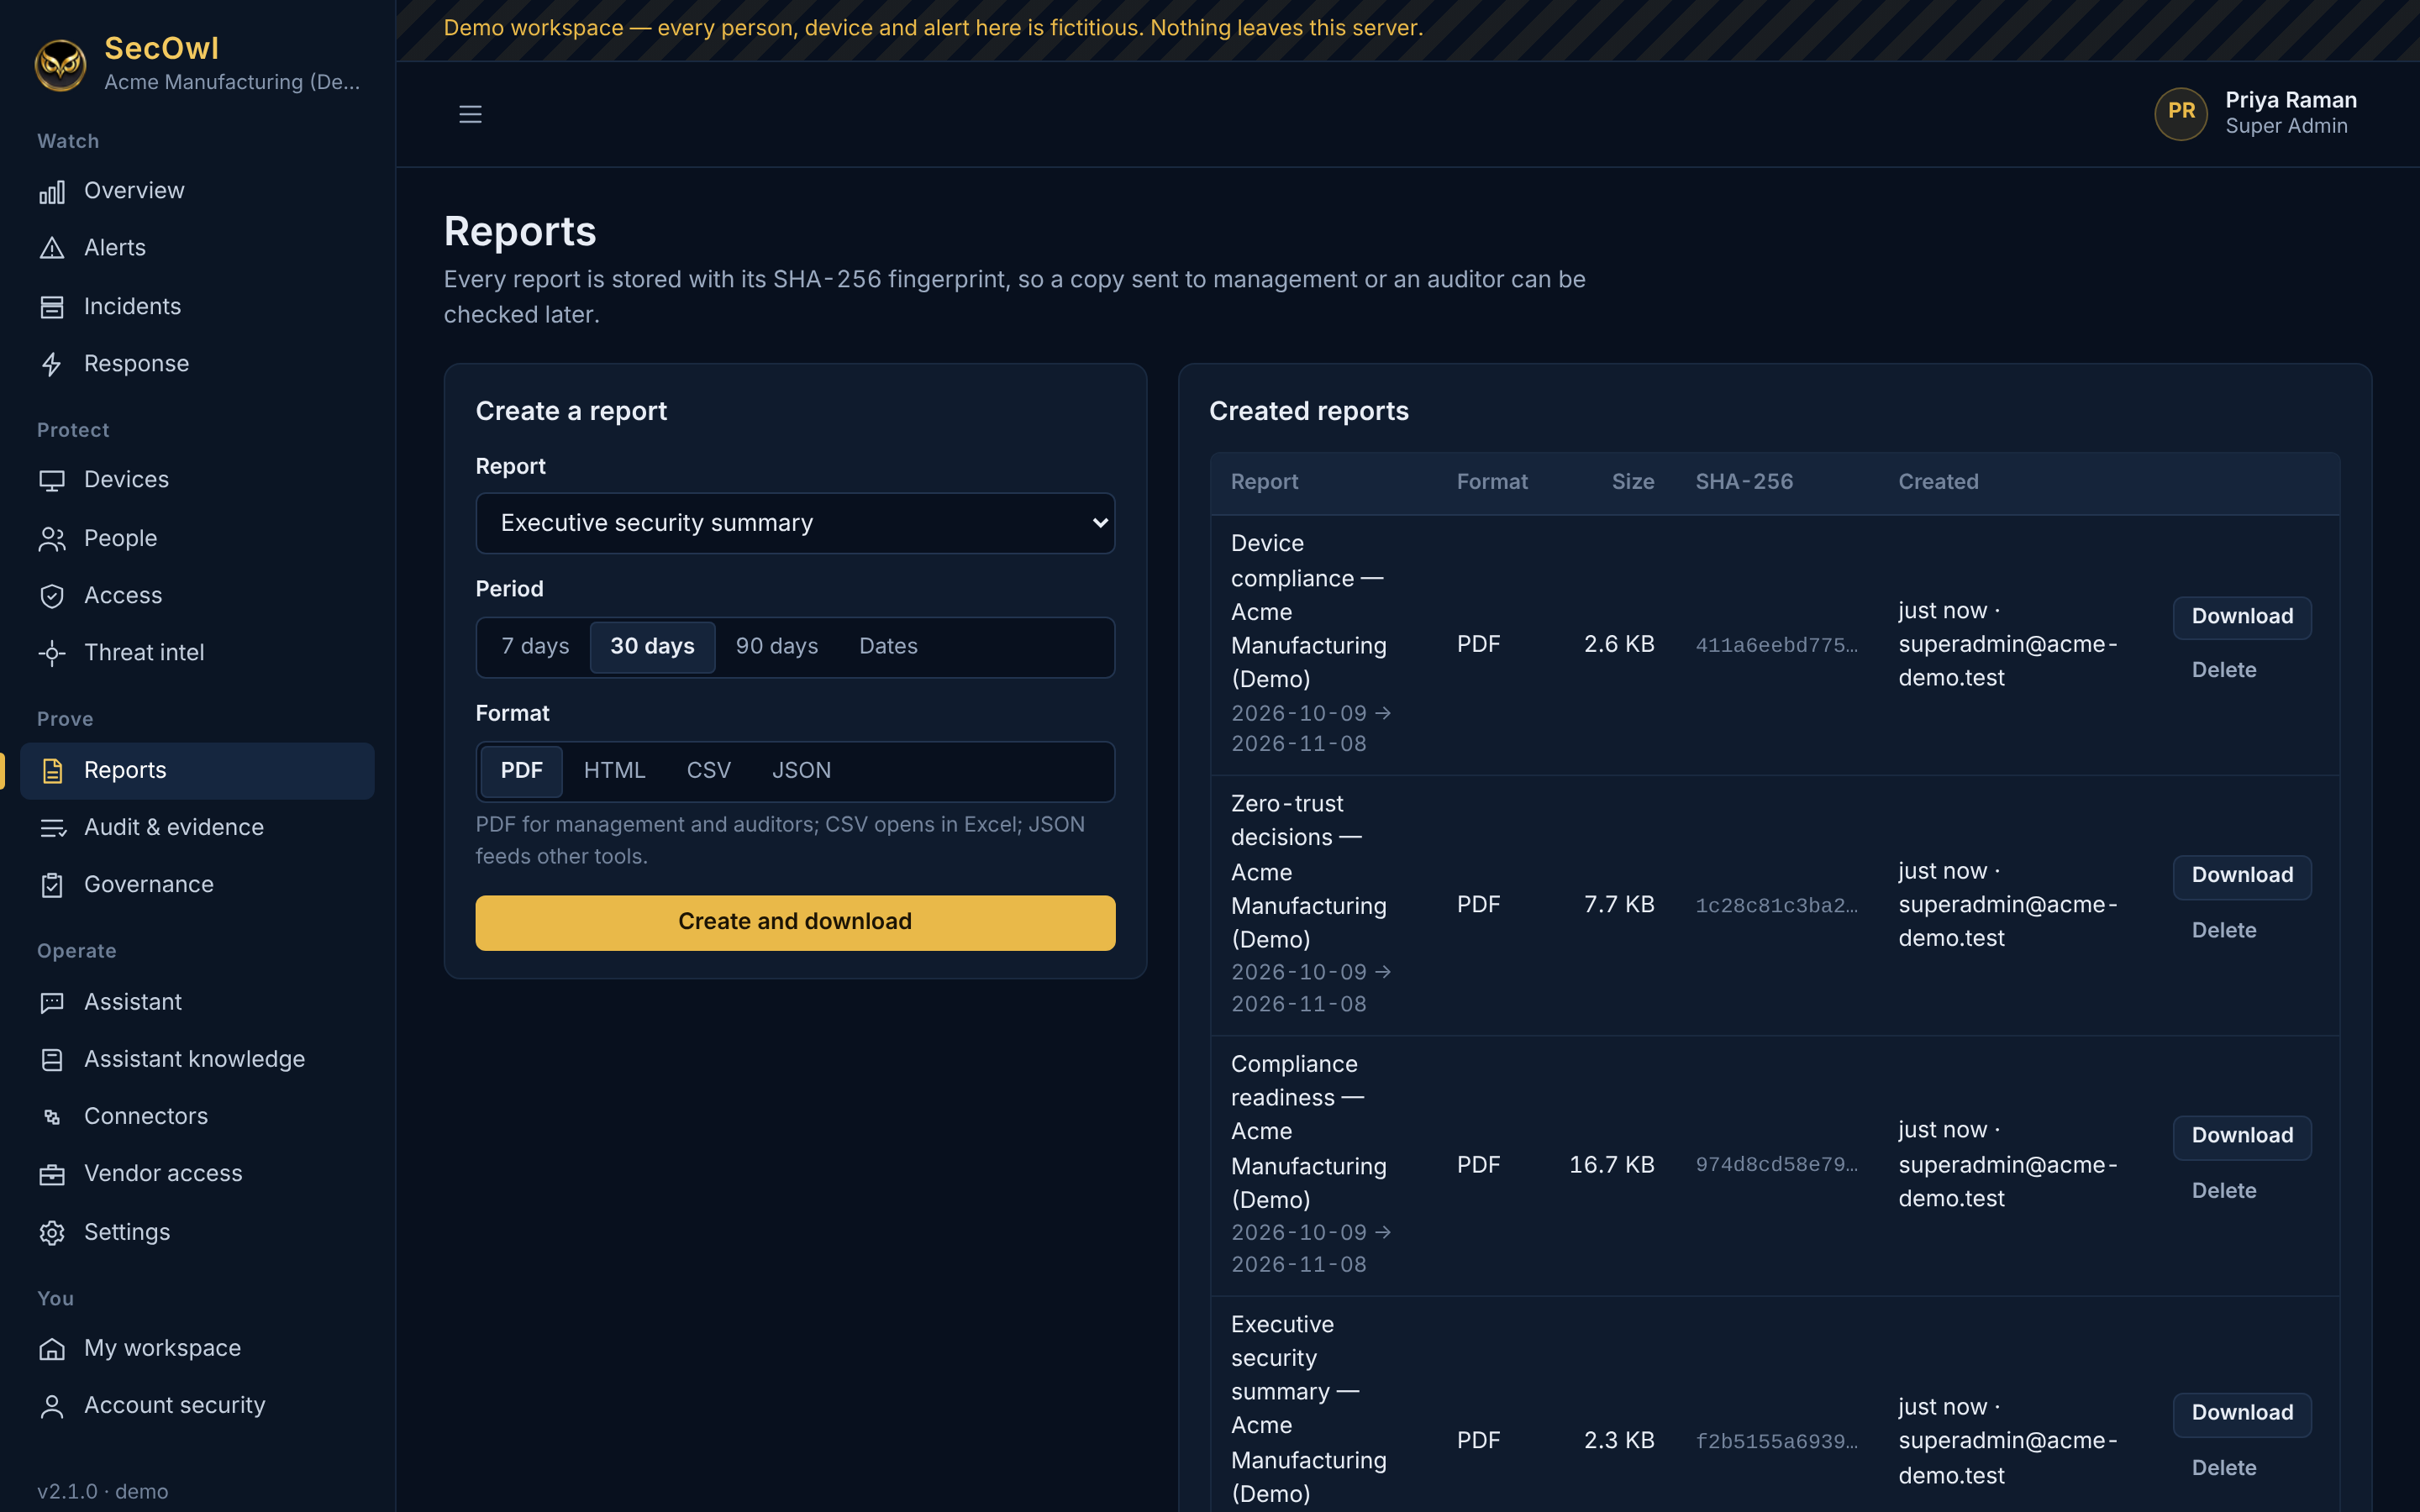
Captured on 8 November 2026 from SecOwl 2.1.0 running live (demo edition, fresh installation) and SecOwl SOC Hub 2.1.0 with three demo companies. All names, people and devices are fictitious demo data, such as "Acme Manufacturing (Demo)". The screens are not mocked up or retouched.
Earlier proof material
Material published before the SecOwl 2.1 captures above.


